

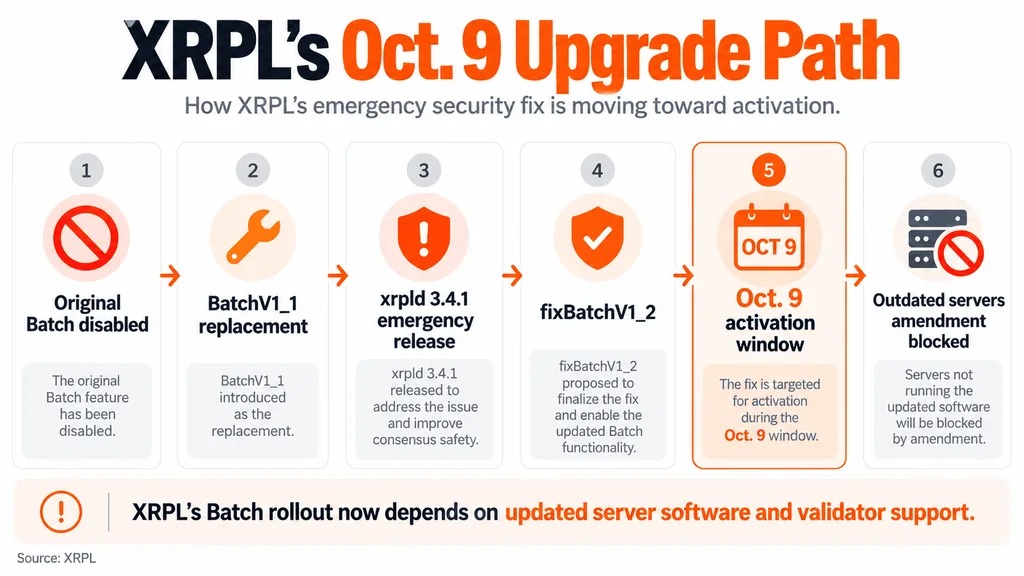
On September 25th, the developers of XRPL released xrpld version 3.4.1 as an emergency update to address what they referred to as "sensitive security-related issues." According to the official release notes, the new fixBatchV1_2 amendment has received the supermajority support of validators. If this support rate continues to remain above the required threshold, it is expected to be activated on October 9th.
For server operators, the importance of this date is not just about gaining a new feature. If the nodes have not been upgraded to version 3.4.1 at the time fixBatchV1_2 is activated, they may fall into the amendment blocked (amendment blocking) state, which means they will no longer be able to stay synchronized with the network.
Batch will arrive along with another security fix.
This security patch is directly related to BatchV1_1. BatchV1_1 is an alternative to the implementation of Batch that was earlier adopted; after developers discovered a critical vulnerability, the original implementation of Batch was abandoned.
Batch Transactions allow multiple operations to be packaged together, including a structure where "either all are successful or the entire operation fails." Coinpaper As previously explained, Batch The upgrade was originally scheduled for September but was postponed to October. However, since the support rate of validators briefly fell below the required level, the two-week countdown for this upgrade was reset.
XRPL Official amendment document confirms that BatchV1_1 has replaced the initial Batch amendment and explicitly fixed a critical vulnerability identified in earlier implementations.
The complete details of the security issue have not yet been made public.
What makes this emergency release unusual is that the developers have not yet made available the source code that includes these security-related fixes.
XRPL indicates that the relevant code will be disclosed later along with a review note to explain this issue. The currently released update log confirms that the fixes include: rejecting internal transactions that use the incorrect wrapper Batch, as well as providing additional reinforcement for integer operations in the payment engine and ledger auxiliary tools.
This does not mean that XRP Ledger has already been exploited. Official announcements have not reported any theft of funds or attacks on the mainnet; this update seems to be a preventive measure.
This activation itself is still conditional. The changes to the XRPL protocol require continuous support from verifiers, and cannot be unilaterally activated by Ripple. Coinpaper explains this process in its guidelines regarding the governance of XRPL.
Marcus Hale
Marcus Hale is a journalist specializing in cryptocurrency and financial markets, covering topics such as Bitcoin, Ethereum, digital assets, regulation, ETF, and the adoption by institutions. His work focuses on driving market developments, investor trends, and shaping the broader forces of the crypto economy.