














Ransomware gang n0n leaked customer data related to Visa, Mastercard, and JPMorgan through a third-party supplier.
It is reported that over 6,000 high-end customers of Visa have been affected, with the relevant data coming from a service provider in the Asia-Pacific region.
Visa, Mastercard, and JPMorgan have all confirmed that their core systems and payment networks have not been compromised.
A ransomware gang leaked thousands of customer records related to three giants in the financial industry: Visa, Mastercard, and JPMorgan Chase. The leak on November 19 did not breach the core systems of these companies, but it exposed third-party suppliers responsible for marketing and benefits programs.
At the same time, it is possible that over 22,000 customers have been affected, including 16,000 cardholders of JPMorgan Reserve.
Hackers gain access through the "backdoors" of major financial institutions
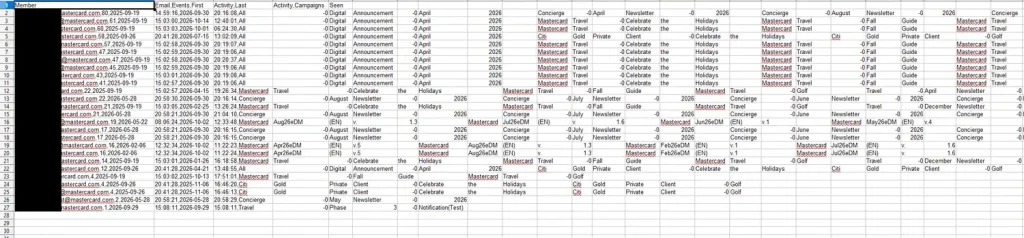
This attack did not originate from within Visa, Mastercard, or JPMorgan. On the contrary, the ransomware gang n0n targeted third-party service providers that are connected to these three financial companies.
Surveys of the n0n activity have revealed that the gang typically obtains access rights through weak or stolen credentials. After gaining access to the supplier's systems, the attackers are alleged to have extracted databases containing customer loyalty, dining, and marketing records.
The initial signs of this operation appeared on November 9th, when n0n added a new "Company #150" list to their ransom website based on Tor. By November 16th, the gang had named Visa, Mastercard, and JPMorgan and set a 48-hour deadline for the ransom to be paid.
16,000 JPMorgan customers are among those affected.
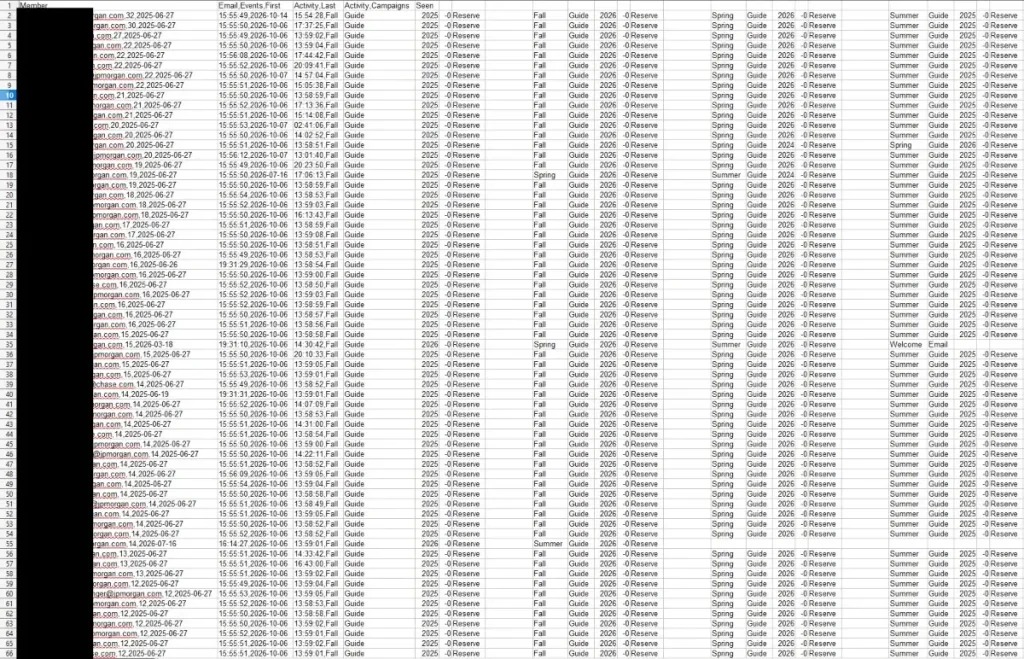
The information that was leaked varied among the three companies, but this data is mainly related to customer marketing and welfare programs, rather than payment processing.
Marketing information of approximately 16,000 JPMorgan Reserve cardholders has been exposed, which may include names and email addresses. Over 6,000 high-end Visa customers have been affected, and the relevant data comes from a third-party supplier operating in the Asia-Pacific region.
Mastercard indicates that a small amount of information belonging to customers who are part of a specific welfare program has also been exposed.
However, there is one important detail that distinguishes this incident from a direct intrusion into the payment system: no card numbers or payment data were leaked.
JPMorgan, Visa and Mastercard respond to the leakage incident
In response to this attack, JPMorgan stated on X that a third party providing services to the company was also affected by the attack.
"Our services have not been affected."
The company also added that affected customers will receive support, including free credit monitoring services.
Visa indicates that this incident involves a service provider in the Asia-Pacific region, and it emphasizes that its own systems were not affected. The company also stated that there is no indication that any sensitive payment information was leaked.
Mastercard indicates that the leak has been brought under control, and it is also confirmed that its payment network has not been affected.
This incident indicates that hackers do not need to directly break into Visa, Mastercard, or JPMorgan. They found an entry point by obtaining access through companies that hold customer-related information.